
Your journey to digital security maturity starts here
We help companies prevent, detect, and respond to cyber threats with efficiency and clarity. We work as an extension of your team, delivering personalized solutions aligned with your needs and your company's current moment.
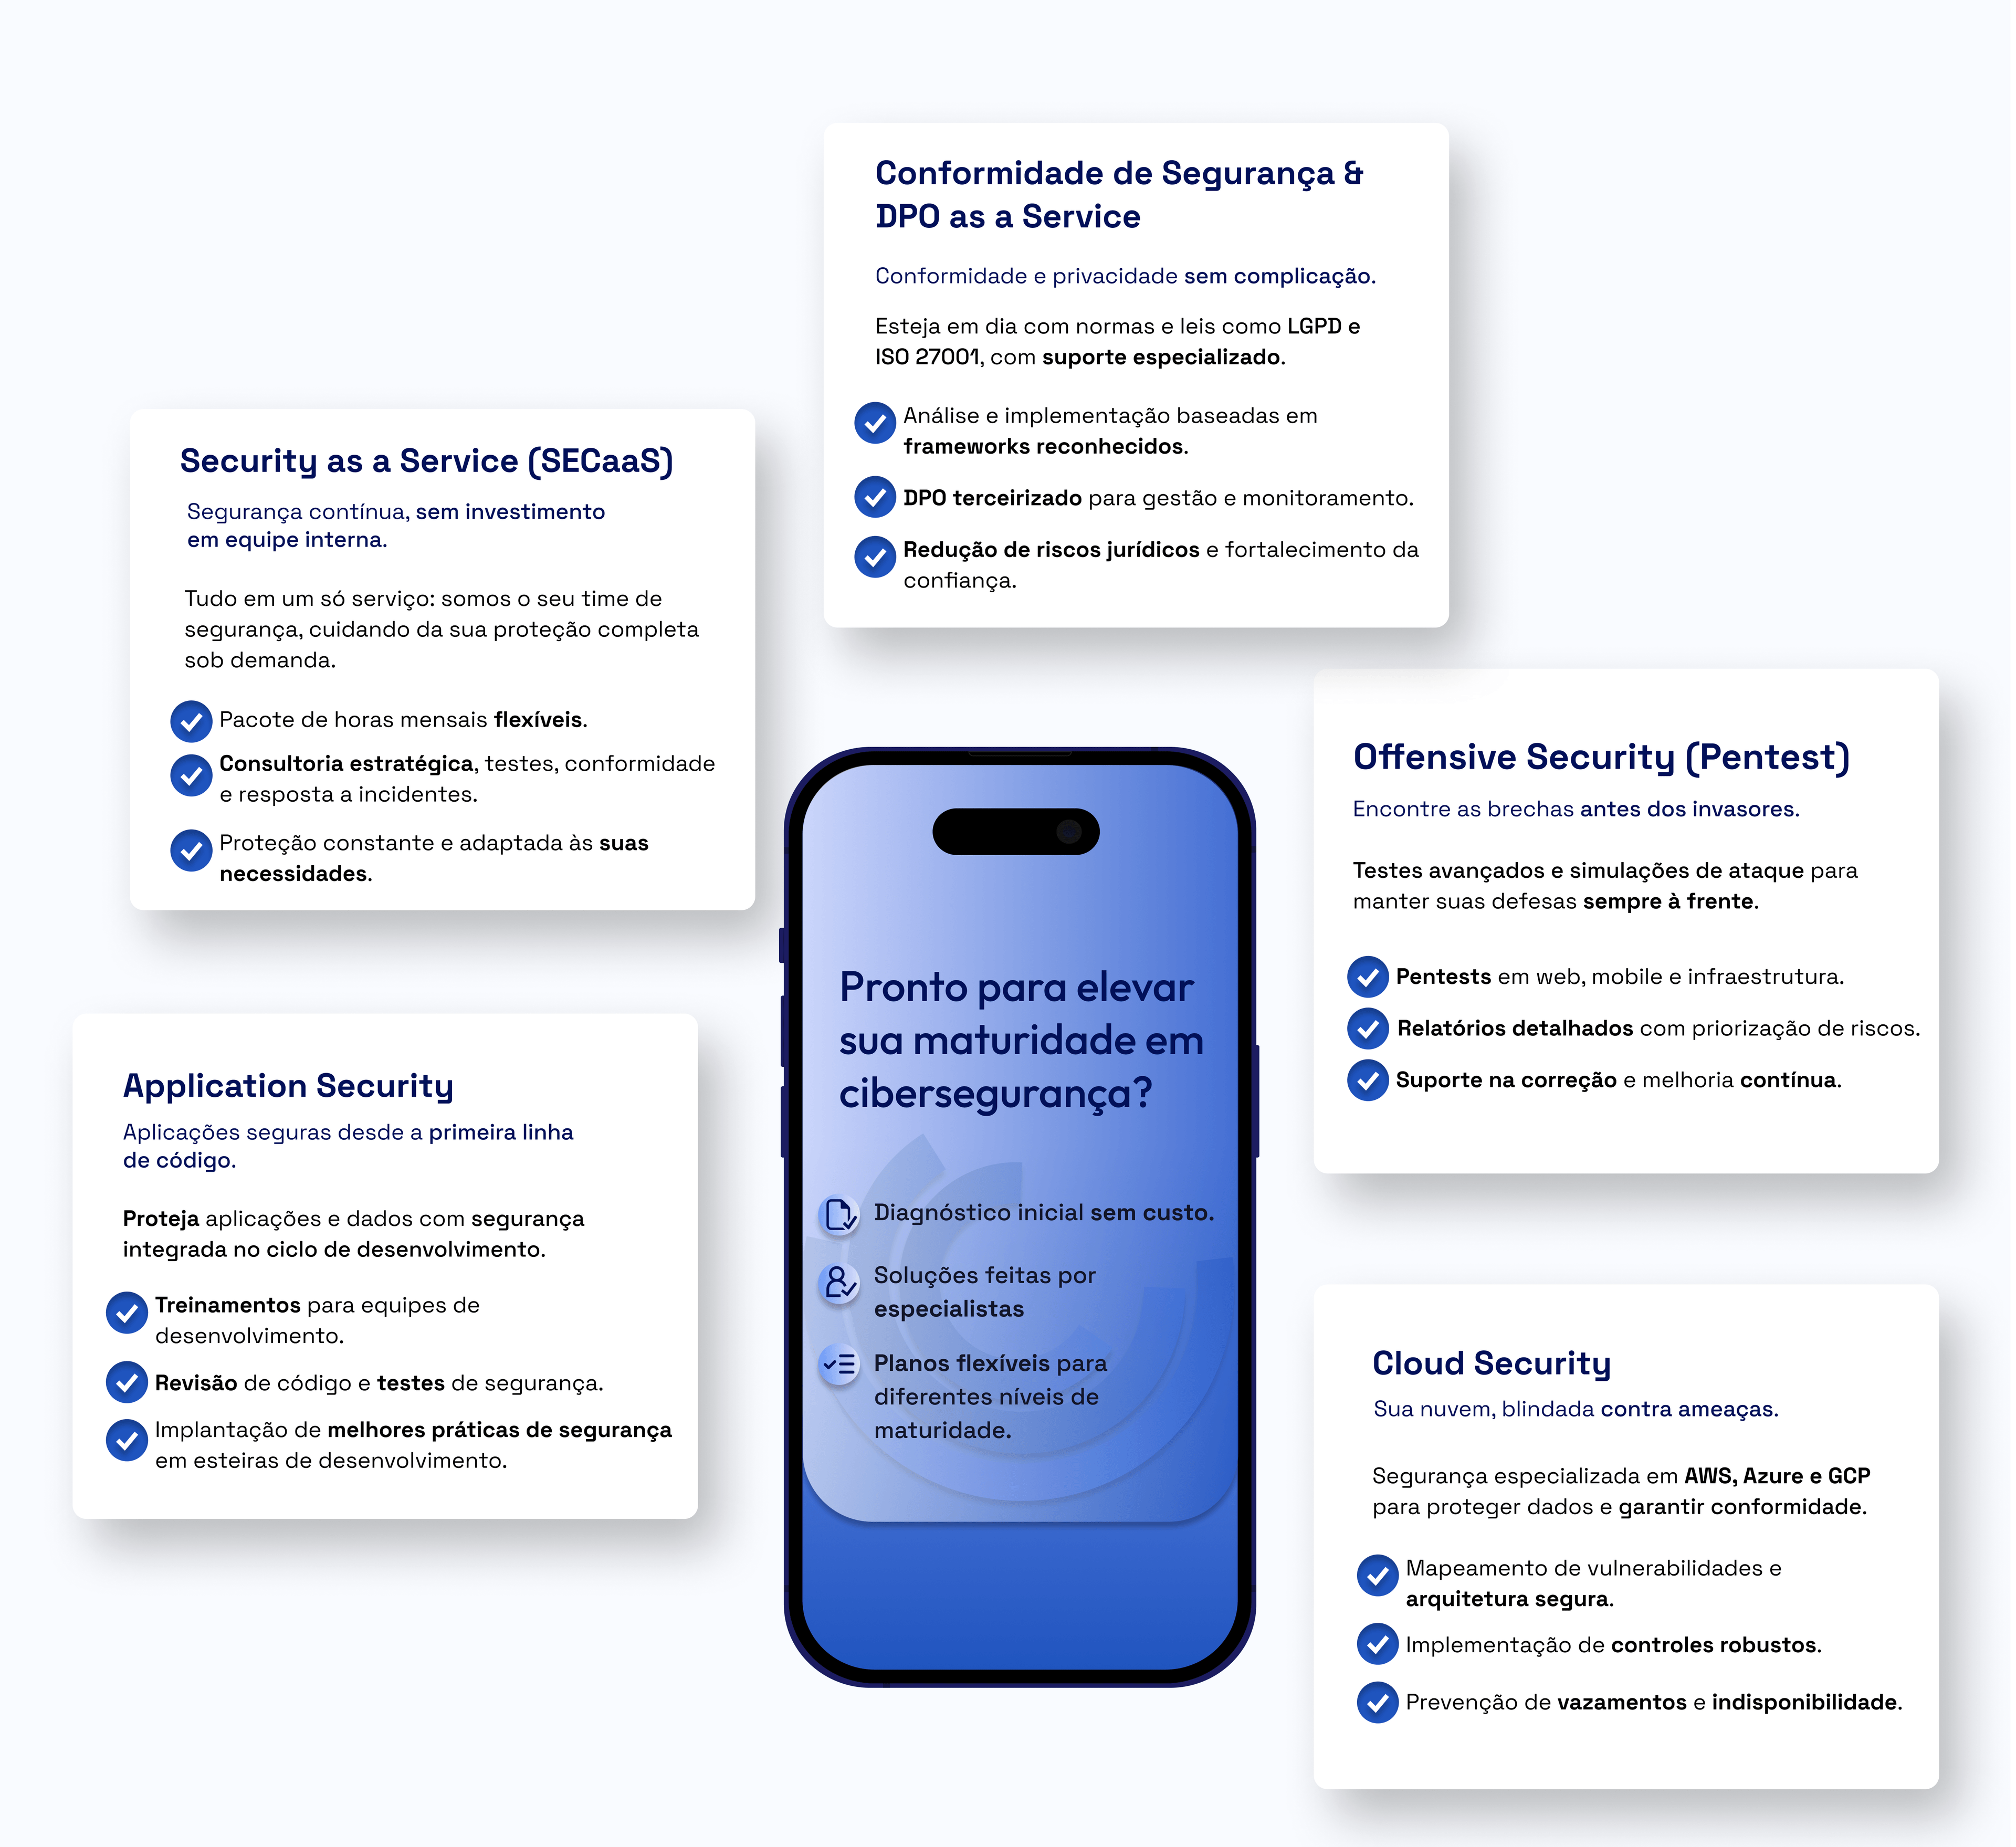
Security as a Service (SECaaS)
Continuous security, without investing in an in-house team.
Everything in one service: we are your security team, taking care of your complete protection on demand.

Flexible monthly hour packages.
Strategic consulting, testing, compliance and incident response.
Constant protection adapted to your needs.
Security Compliance & DPO as a Service
Compliance and privacy without complication.
Stay up to date with standards and laws such as LGPD and ISO 27001, with specialized support.
Analysis and implementation based on recognized frameworks.
Outsourced DPO for management and monitoring.
Reduced legal risk and stronger trust.
Offensive Security (Pentest)
Find the gaps before attackers do.
Advanced tests and attack simulations to keep your defenses always ahead.
Pentests on web, mobile and infrastructure.
Detailed reports with risk prioritization.
Remediation support and continuous improvement.
Cloud Security
Your cloud, shielded against threats.
Specialized security on AWS, Azure and GCP to protect data and ensure compliance.
Vulnerability mapping and secure architecture.
Implementation of robust controls.
Prevention of leaks and downtime.
Application Security
Secure applications from the first line of code.
Protect applications and data with security built into the development cycle.
Training for development teams.
Code review and security testing.
Rollout of security best practices in development pipelines.
Some of our success cases:
Cloud Security
The company had no clarity about cloud risks or visibility into access and external exposures. We conducted a complete assessment of cloud environments: IAM, networks, instances, WAF, serverless, Kubernetes, encryption, and backups. We fixed public exposures, removed excessive access, and restructured identity controls. The result was an operation with cloud governance and risks under control.
Application Security
The company was building its banking platform and needed to ensure the product was secure from the start. We worked with DevSecOps from the beginning: architecture review, code analysis, threat modeling, pentests, and developer training. The company launched its application with security integrated into the development process. It avoided rework and passed audits with confidence. It gained agility and reputation in the market.
DPO as a Service
A technology company needed to comply with LGPD, without a dedicated team and under pressure from partners to prove compliance. We acted as DPO as a Service, conducting gap analysis, creating policies, data processing registration, team awareness, and legal support. The company achieved solid governance, reduced legal risks, and came to be seen as trustworthy and prepared.
Security Compliance
The company began serving contracts with strict security requirements but had no structured view of risks or standardized controls. We conducted a Cybersecurity Assessment based on NIST CSF and CIS Controls v8 frameworks, assessing maturity, risks, and governance. The company gained clarity about its real risks and structured security management aligned with global standards.
Security as a Service
The company needed a robust security structure but had no internal team and didn't want to depend on one-off actions. We acted as a continuous security team, with on-demand specialists for periodic analyses, monitoring, policies, pentests, and incident response. The company integrated security into the business, reduced incidents, and elevated operational maturity.
